Install fraud rarely looks like fraud at first. It looks like a great source: cheap installs, big volume, steady growth. The giveaway is almost always in what happens just before and just after the install.
Why fraud is a network problem
Advertisers usually see fraud weeks later, in retention or revenue reports. By then the installs are billed and the budget is gone. A network sees the traffic first, which makes it the right place to stop it.
The seven signs
1. Installs that arrive seconds after the click
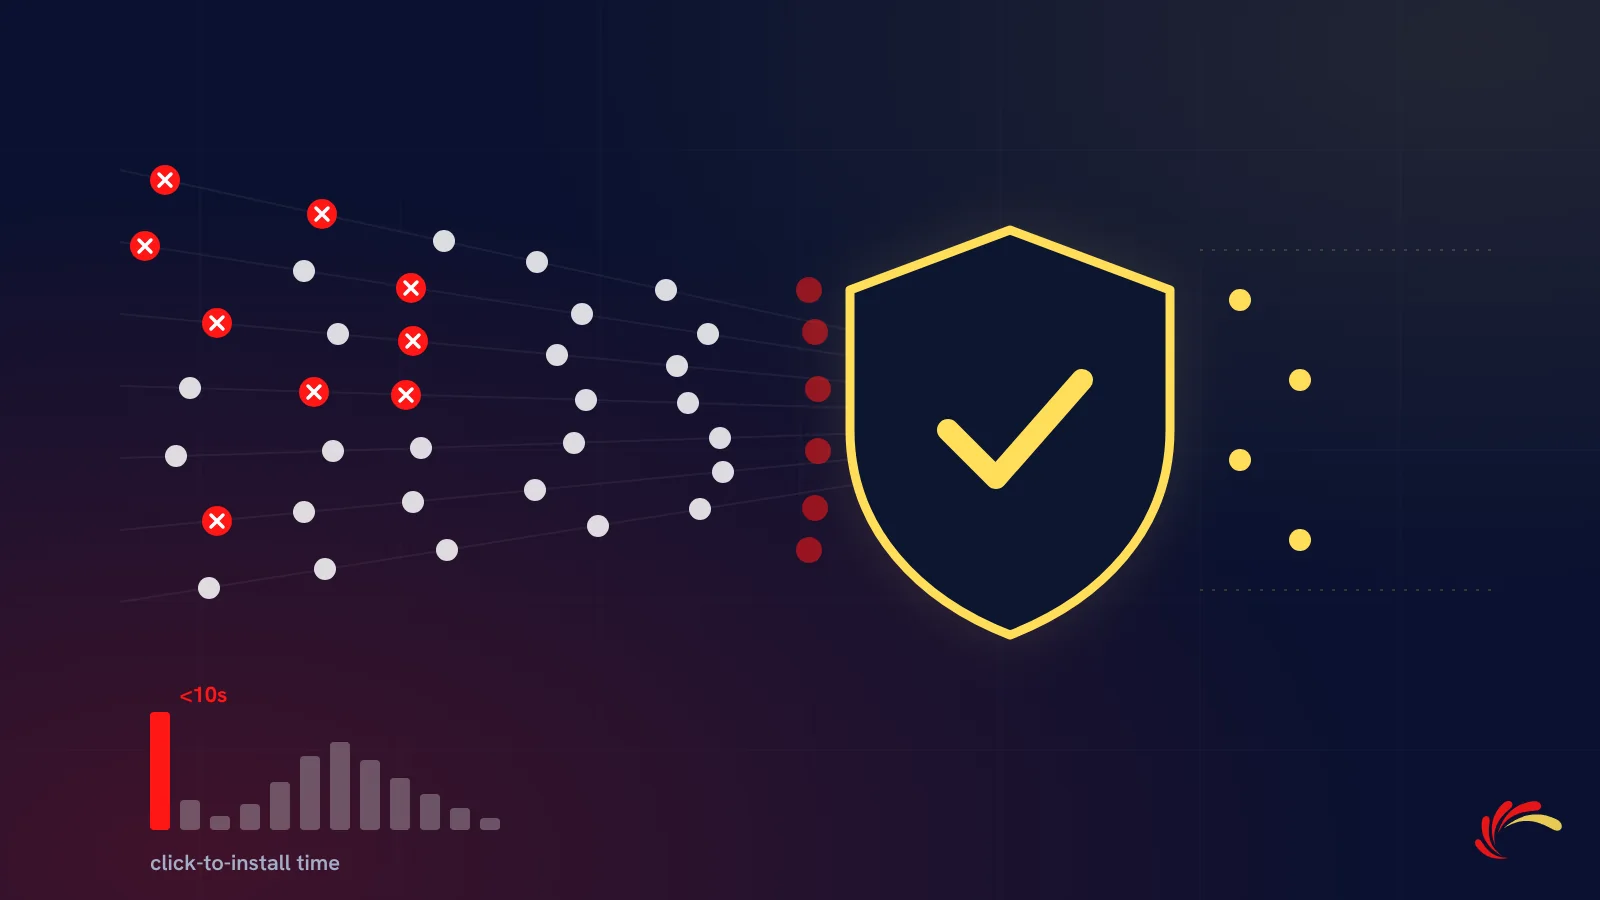
Real users need time to land on the store, download and open the app. A cluster of installs with a click-to-install time of a few seconds often points to click injection, where a click is fired just as an install that was already happening completes, to steal the credit.
2. A long, flat tail of click-to-install times
The opposite pattern: installs spread evenly over hours or days after the click, from sources sending huge click volumes with tiny conversion rates. That is typical of click spamming, where clicks are fired for users who never saw an ad, hoping to claim organic installs.
3. Installs that do nothing afterwards
Bots and device farms can produce installs, but they rarely behave like people afterwards. Near-zero retention, no events, or events at perfectly regular intervals are strong signals.
4. Devices that look too similar
Many installs from the same handful of device models and OS versions, from new or reset devices, or from data-center IP ranges, suggest emulators or farms rather than real audiences.
5. Location that doesn't add up
The IP says one country while the device language, time zone or carrier say another. Heavy VPN or proxy use on a geo-targeted offer is a common cause.
6. Events that are impossible
Purchases with no session before them, events on app versions that were never released, or sequences that skip required steps can indicate SDK spoofing, where installs and events are faked server-side.
7. Sudden spikes from one source
A source that jumps from hundreds to thousands of installs overnight, especially on a non-incentivised offer, deserves a look. Hidden incentives often show up exactly this way, followed by weak engagement.
What a network should do
- Test before launch. Run each offer on in-house inventory first, so you know what normal looks like for that app.
- Reject automatically. Apply rules on click-to-install time, device and IP signals before conversions are counted.
- Be transparent by source. Report results by publisher and sub-ID, so a weak source can be paused without stopping good ones.
- Reconcile monthly. Settle rejections with advertisers and pass them through to publishers before payouts.
At Adperience Media, fraud detection flags and rejects suspicious activity before it reaches the advertiser's budget, and rejected conversions are never paid to publishers.
What you can do
Set clear KPIs in your brief, such as minimum retention or event rates, and share your attribution partner's fraud reports with your network. The faster both sides see the same signals, the faster bad sources get cut.